Dark Web Hackers List
This resource is designed for cybersecurity beginners and researchers seeking insights into dark web hackers and their aliases.
A dark web hackers list is a reference to publicly documented cybercrime actors, aliases, and groups, not a directory of verified .onion sites. We classify convicted figures such as BreachForums founder "pompompurin"[1], alleged identities such as "IntelBroker"[2] and "LockBitSupp"[3], and organisations such as LockBit, while treating leak-site victim claims as unverified because they may be selective or delayed[4].
Dark Web Hackers Evidence Matrix
- Name/Alias
- pompompurin
- Connection
- BreachForums founder
- Active Years
- 2020-2026
- Status
- Convicted
- Confidence Level
- High
- Last Verification
- 2026
- Primary Sources
- [1]
- Name/Alias
- IntelBroker
- Connection
- Stolen data seller
- Active Years
- 2020-2025
- Status
- Charged
- Confidence Level
- Medium
- Last Verification
- 2025
- Primary Sources
- [2]
- Name/Alias
- LockBitSupp
- Connection
- LockBit operator
- Active Years
- 2020-2023
- Status
- Charged
- Confidence Level
- High
- Last Verification
- 2023
- Primary Sources
- [3]
- Name/Alias
- LockBit
- Connection
- Ransomware group
- Active Years
- 2019-Present
- Status
- Active
- Confidence Level
- High
- Last Verification
- Depends on activity
- Primary Sources
- [3]
- Name/Alias
- Evgenii Ptitsyn
- Connection
- Phobos ransomware admin
- Active Years
- 2020-2026
- Status
- Convicted
- Confidence Level
- High
- Last Verification
- 2026
- Primary Sources
- [5]
- Name/Alias
- Kai West
- Connection
- Data seller
- Active Years
- 2020-2025
- Status
- Charged
- Confidence Level
- Medium
- Last Verification
- 2025
- Primary Sources
- [2]
- Name/Alias
- Connor Moucka
- Connection
- Hacking conspiracy
- Active Years
- 2020-2026
- Status
- Convicted
- Confidence Level
- High
- Last Verification
- 2026
- Primary Sources
- [6]
- Name/Alias
- Dmitry Khoroshev
- Connection
- LockBit operator
- Active Years
- 2020-Present
- Status
- Charged
- Confidence Level
- High
- Last Verification
- Depends on activity
- Primary Sources
- [3]
What “Dark Web Hacker” Actually Means
The terms associated with the dark web can be confusing, so we clarify some key definitions. The dark web refers to a portion of the internet that is intentionally concealed and typically requires special software, like Tor, to access. In contrast, the deep web consists of content not indexed by conventional search engines, which includes databases and private corporate information[7]. An onion service is a specific type of website that uses the .onion domain, reachable only through the Tor network, which provides anonymity and end-to-end encryption[8].
A hacker is a person who uses technical skills to gain unauthorized access to systems or networks, often classified as either a black-hat hacker (malicious intent), white-hat hacker (ethical hacking), or gray-hat hacker (operating in a morally ambiguous space). The distinction is crucial; black-hat hackers engage in cybercrime, while white-hat hackers help organisations secure their systems[7].
It's important to note that a hacker may utilise dark-web infrastructure without being exclusively based there. Many notorious hackers often cited in discussions about cybercrime do not have documented connections to the dark web. For example, while ransomware groups like LockBit operate on the dark web, individual hackers may not necessarily be tied to that environment[3].
Understanding these definitions helps clarify the landscape of cyber threats. For beginners and researchers, recognising these distinctions can aid in identifying potential threats and navigating the complexities of the dark web and its actors.
Dark Web Hackers List at a Glance
We have compiled a reference table of notable dark web hackers, detailing their aliases, connections, activities, and current statuses. This sortable matrix provides a clear overview of key actors within the cybercrime sphere, including their documented connections to the dark web and verifiable information regarding their operations.
| Name/Alias | Connection | Active Years | Status | Confidence Level | Last Verification | Primary Sources |
|---|---|---|---|---|---|---|
| pompompurin | BreachForums founder | 2020-2026 | Convicted | High | 2026 | [1] |
| IntelBroker | Stolen data seller | 2020-2025 | Charged | Medium | 2025 | [2] |
| LockBitSupp | LockBit operator | 2020-2023 | Charged | High | 2023 | [3] |
| LockBit | Ransomware group | 2019-Present | Active | High | Depends on activity | [3] |
| Evgenii Ptitsyn | Phobos ransomware admin | 2020-2026 | Convicted | High | 2026 | [5] |
| Kai West | Data seller | 2020-2025 | Charged | Medium | 2025 | [2] |
| Connor Moucka | Hacking conspiracy | 2020-2026 | Convicted | High | 2026 | [6] |
| Dmitry Khoroshev | LockBit operator | 2020-Present | Charged | High | Depends on activity | [3] |
This table is designed to provide a snapshot of significant players in the dark web landscape, reflecting their documented activities and current legal standings. It is essential to verify the latest status and activities of these individuals and groups, as the dark web is a rapidly evolving environment where actors may change their operations or legal statuses frequently. Always consult reliable sources for the most current information.
Notable Individuals and Aliases Linked to Dark-Web Forums
Several individuals and aliases have made significant impacts within dark-web forums and cybercrime circles. Below is a concise overview of notable actors, their roles, and documented connections to cybercrime.
pompompurin
Known as the founder of BreachForums, "pompompurin" grew the platform to over 330,000 members before his arrest. He was convicted for access-device offenses and possession of child sexual abuse material, receiving a three-year prison sentence in 2026. His forum facilitated the exchange of stolen data, highlighting the challenges of cybersecurity in protecting sensitive information[1].
IntelBroker
The alias "IntelBroker" is attributed to a British national, Kai West, who allegedly sold stolen data approximately 41 times for profit and offered it for free or for forum credits 117 times. The Justice Department claimed his actions caused damages exceeding $25 million. As of June 2025, he faced charges related to these activities, but his legal status remains disputed[2].
LockBitSupp
Dmitry Khoroshev, linked to the alias "LockBitSupp," has been charged with operating the LockBit ransomware, which reportedly attacked over 2,500 victims across 120 countries, extracting at least $500 million in ransom payments. The U.S. authorities have closely monitored his activities, reflecting the significant threat posed by ransomware groups in the dark web landscape[3].
Evgenii Ptitsyn
As the administrator of Phobos ransomware, Evgenii Ptitsyn pleaded guilty in March 2026. His operations resulted in over 1,000 victims and approximately $39 million in ransom payments. This case underscores the operational capabilities of ransomware administrators on dark web platforms, where coordination occurs via onion services[5].
Connor Moucka
Connor Moucka was involved in a hacking conspiracy that compromised at least 165 organisations, generating more than $2.5 million in ransom payments. He advertised stolen data on various platforms, including BreachForums. He pleaded guilty in August 2026, demonstrating the real-world consequences of cybercrime[6].
These profiles illustrate the diverse roles and impacts of individuals operating within dark-web forums. Each case not only highlights the individuals' alleged or confirmed activities but also reflects broader trends in cybercrime, including data breaches and ransomware operations. For ongoing research, it is crucial to consult reliable sources to verify the current status of these actors, as the landscape continues to evolve rapidly.
Notable Hacker Groups with Dark-Web Operations
Numerous hacker groups operate within the dark web, offering various services such as ransomware, data trading, and access brokering. Below, we profile some of the most notable groups, detailing their operations, documented campaigns, and current statuses.
LockBit
LockBit is a prominent ransomware group first identified in 2019. It has been linked to over 2,500 attacks across 120 countries, extracting at least $500 million in ransom payments. The group operates on a ransomware-as-a-service model, allowing affiliates to conduct intrusions while retaining 80% of the ransom, with the developers taking a 20% cut. LockBit remains active as of 2023[3].
Cl0p
Cl0p is another significant ransomware group, noted for its targeted attacks against high-profile organisations. It first emerged around 2020, with documented campaigns that included the exploitation of vulnerabilities in various systems to deploy ransomware. Cl0p is associated with data leaks, often publishing stolen information on its leak site to pressure victims into paying. The group continues to operate, adapting its tactics in response to law enforcement actions[3].
ALPHV/BlackCat
ALPHV, also known as BlackCat, surfaced in late 2021. This group is distinct for its use of the Rust programming language, making it a sophisticated ransomware variant. ALPHV has been involved in several high-profile attacks, utilising data leaks as a bargaining tool for ransom payments. The group remains operational, showing resilience against law enforcement efforts[3].
REvil
REvil, also known as Sodinokibi, was highly active until its alleged takedown by law enforcement in 2021. This group was notorious for its double extortion tactics, where it not only encrypted victim data but also threatened to release sensitive information. Although its operations have been disrupted, remnants of the group have resurfaced, indicating a potential ongoing threat[3].
Conti
Conti was a well-known ransomware group that operated from 2020 until its collapse in early 2022. The group was responsible for numerous high-profile attacks and had a reputation for swift ransom negotiations. Following a major leak of internal communications, many of its members have been identified or apprehended, but some aspects of its operations may still persist[3].
ShinyHunters
ShinyHunters is primarily known for data breaches rather than ransomware. Emerging in 2020, this group has been involved in various high-profile data breaches, selling stolen data on dark web forums. Their operations highlight the increasing trend of data trading in cybercrime, and they continue to be active, seeking new targets for their data theft[3].
Qilin
Qilin is a less known but emerging group that has been linked to both ransomware and data trading. Their activities began to surface around 2022, with a focus on exploiting vulnerabilities in corporate networks. While their current status is less documented than others, they represent the evolving landscape of cyber threats that researchers should monitor[3].
These hacker groups exemplify the range of activities and threats present in the dark web. Each operates with distinct methodologies and objectives, making it essential for cybersecurity professionals and researchers to stay informed about their developments and tactics.
Their Contributions and Impact on Cybersecurity
The actions of dark web hackers have prompted significant shifts in cybersecurity practices, incident response strategies, and even international law enforcement cooperation. While many activities are criminal in nature, the repercussions of these actions have led to advancements in defensive measures and policy reforms.
For instance, the rise of ransomware groups such as LockBit has forced organisations to reassess their backup strategies and incident response protocols. LockBit has reportedly attacked over 2,500 victims across 120 countries, extracting at least $500 million in ransom payments[3]. In response, businesses have begun adopting more robust backup solutions and implementing multi-factor authentication to mitigate the risks posed by such attacks. This shift emphasises the importance of proactive cyber hygiene among organisations.
Additionally, the operations of notorious hackers have highlighted vulnerabilities in existing frameworks for vulnerability disclosure. The Justice Department's actions against individuals like Kai West, who sold stolen data and caused damages exceeding $25 million, have underscored the need for enhanced reporting mechanisms and collaboration between private sectors and law enforcement[2]. This has led to initiatives that promote responsible disclosure, where security researchers can report vulnerabilities without fear of legal repercussions, thereby fostering a more secure digital environment.
Moreover, documented incidents involving black-hat hackers have influenced international cooperation among law enforcement agencies. The takedown of major cybercrime forums, as seen with the operation against LeakBase, involved collaboration across 14 countries and showcased the effectiveness of coordinated efforts in combatting cybercrime[9]. This has resulted in the establishment of multinational task forces dedicated to tracking and apprehending cybercriminals, further strengthening global cybersecurity efforts.
These examples illustrate that while the activities of dark web hackers are predominantly harmful, their impact has also catalysed meaningful changes in cybersecurity practices and policies, driving the evolution of defensive strategies and international cooperation in the fight against cybercrime.
How Hacker Forums, Leak Sites, and Onion Links Fit Together
Cybercrime forums, data-leak sites, and onion links are interconnected components of the dark web ecosystem that facilitate various illicit activities. Cybercrime forums serve as platforms where threat actors communicate, share information, and recruit affiliates. These forums vary in size and can include both deep web and dark web sites, with some operating openly while others remain concealed. For instance, LeakBase, a notable cybercrime forum, had over 142,000 members before its seizure in 2026, showing the scale at which such forums can operate[9].
Data-leak sites are primarily used to publish stolen data, applying public pressure on victims to pay ransom. These sites often feature a selection of victims, which may not represent the total number of attacks, as they sometimes list only those chosen for exposure[4]. Ransomware-as-a-service (RaaS) models allow individuals to deploy ransomware without needing advanced technical skills, enabling a broader range of actors to participate in cybercrime[3]. Initial access brokers play a crucial role in this model, selling access to compromised networks, thus creating a marketplace for cybercriminal activities.
Onion links, accessible exclusively through the Tor network, are vital for maintaining the anonymity of both users and services. They use the .onion domain, which conceals the location and identity of the host[8]. While these links can lead to legitimate uses of Tor, such as privacy protection, they also host many illegal activities. The distinction between operators, vendors, affiliates, and administrators is essential; each has different roles within this ecosystem. For example, ransomware operators develop malware and manage the infrastructure, while affiliates carry out the actual intrusions and negotiations with victims[3].
Actors within this space utilise these services for reputation building, recruitment, negotiation, and publicity. A forum administrator may maintain a platform's integrity and attract new members by enforcing rules, while vendors offer services or stolen data, and affiliates execute attacks. This collaborative environment enhances the operational capabilities of cybercriminals, allowing them to expand their reach and effectiveness in the dark web landscape.
How to Verify Hacker Names, Claims, and Onion Links
Verifying the identities and claims of hackers operating in the dark web is crucial for researchers and cybersecurity professionals. We recommend a source-validation checklist that includes the following elements: court records, notices from the Department of Justice (DOJ), FBI, and Europol, sanctions lists, established security research, archived web pages, and corroborated news reporting. Each of these sources can provide valuable insights into the legitimacy of a hacker's claims and activities.
Common attribution problems can complicate verification. Recycled aliases are a frequent issue, where hackers change their names to evade detection. False flags and rebranding can mislead researchers into attributing actions to the wrong individuals or groups. Exaggerated breach claims are another risk; hackers may inflate the significance of their activities to gain reputation or leverage. Additionally, seized or phishing mirrors can misrepresent the status of a service or actor, leading to incorrect assumptions about their operational capabilities.
To ensure thorough verification, we advise recording the publication date, source type, and confidence level for every profile. This practice helps establish a timeline of events and assess the reliability of the information. For instance, if a hacker's identity is confirmed through multiple law enforcement sources but is also reported in an unverified forum, the confidence level should reflect that discrepancy. Engaging with established security research can provide context; for example, the Congressional Research Service differentiates between the deep web and the dark web, which can inform the understanding of various actors[7].
When verifying .onion links, we recommend confirming them through HTTPS-authenticated official websites or their Onion-Location announcements. Relying on third-party directories can lead to encountering impersonators, as the Tor Project cautions against trusting vanity addresses that seem legitimate but are fraudulent[10][11]. By adhering to this checklist and being mindful of these common pitfalls, we can build a more accurate understanding of the dark web's complex landscape.
Fake Hackers for Hire, Impersonators, and Safety
Many profiles claiming to be hackers for hire on social media or onion sites are often advance-fee scams, recovery scams, or extortion attempts. These impersonators typically lure victims with promises of guaranteed results, often demanding payment in cryptocurrency upfront. This payment method is favoured as it offers anonymity, making it difficult for victims to trace their funds once sent. Common warning signs include claims of "guaranteed success" and pressure tactics urging individuals to share sensitive credentials quickly.
It is essential to recognise these red flags. For instance, if a hacker claims to have a perfect track record, it is likely fabricated. Scammers often copy reputation proofs from legitimate sources, further complicating verification efforts. If you encounter a profile that insists on crypto-only prepayment or exhibits high-pressure sales tactics, exercise caution. These are strong indicators of a scam, especially if the hacker does not provide verifiable references or a legitimate service history.
In the event of exposure to these scams or extortion attempts, we recommend taking immediate defensive actions. First, preserve all evidence, including screenshots of conversations, payment receipts, and any other relevant documentation. This information can be crucial for law enforcement investigations. Next, contact the appropriate authorities, such as local law enforcement or cybercrime units, to report the incident. Additionally, if you have shared sensitive data, consider monitoring your accounts for unusual activity and changing your passwords.
Being vigilant and informed about the tactics employed by these impersonators can significantly reduce the risk of falling victim to their schemes. Always verify the legitimacy of any hacker or service before engaging, especially in the murky waters of the dark web.
Common Mistakes and Misconceptions
Calling Every Notorious Hacker a "Dark Web Hacker"
Fame, criminal activity, or frequent appearance in search results does not prove that an actor operated through the dark web. We require documented links to an onion service or another concealed Tor-based venue, since onion services use the special .onion domain and are accessible only through Tor[8]. Without that evidence, we describe the person by their documented activity rather than applying a broader label.
Mixing Individuals, Aliases, Groups, and Ransomware Brands
Flat lists often place personal identities, screen names, collectives, malware brands, administrators, and affiliates in one category. This obscures responsibility because ransomware developers may maintain infrastructure while separate affiliates conduct intrusions[3]. We assign each entry a clear type and preserve uncertainty where one name may refer to both an alias and an operation[3].
Presenting Attribution as Settled Fact
Short profiles often remove legal qualifiers such as "alleged", "charged", or "pleaded guilty", making different evidence levels appear equivalent. For example, authorities described Dmitry Yuryevich Khoroshev as LockBit's alleged operator, whereas Evgenii Ptitsyn pleaded guilty to administering Phobos ransomware[3][5]. We retain the source's exact attribution language and record whether identification rests on allegations, court findings, or corroborated research.
Assuming Historical Entries Are Still Active
Copied lists can preserve defunct services, abandoned aliases, or addresses that no longer function, creating a false impression of current activity. This is especially visible with obsolete version 2 onion addresses, which used 16 characters, while current version 3 addresses contain 56 letters and numbers before .onion[8]. We separate historical status from current status and add a last-verification field rather than treating an old listing as live evidence.
Confusing Venue Use With Venue Control
An actor posting on a forum does not automatically become its administrator, owner, or representative. Connor Riley Moucka advertised stolen data on BreachForums, Exploit.in, XSS.is, and Telegram, but venue usage alone does not establish control over those platforms[6]. We record the observed action separately from the actor's role, preventing a vendor or poster from being mislabelled as an operator.
Conclusions
- We recommend classifying every entry as an individual, alias, collective, malware brand, affiliate, administrator, or service before comparing actors.
- Treat attribution as graded evidence: distinguish allegations, charges, convictions, self-promotional claims, and findings corroborated by independent security research.
- Check activity dates and current status rather than assuming an old profile, forum account, or onion service remains operational.
- Record what an actor did on a platform separately from who controlled that platform; posting, selling, recruiting, and administering are different roles.
- Begin with source provenance, confidence level, and defensive relevance, not notoriety or unverifiable claims of technical capability.
Next, use our Dark Web Hacking guide to organise these actors by methods, roles, and observable risks.
Where this comes from
- Founder of One of World's Largest Hacker Forums Resentenced to Three Years in Prison
- Serial Hacker “IntelBroker” Charged For Causing $25 Million In Damages To Victims
- U.S. Charges Russian National with Developing and Operating LockBit Ransomware
- Understanding Ransomware Threat Actors: LockBit
- Russian Ransomware Administrator Pleads Guilty to Wire Fraud Conspiracy
- Canadian pleads guilty to hacking U.S. cloud storage provider and extorting its customers for millions
- Dark Web — Congressional Research Service Report R44101
- Understanding and using onion services in Tor Browser
- United States Leads Dismantlement of One of the World's Largest Hacker Forums
- HTTPS for your Onion Service
- Vanity Addresses
 Verified Dark Web LinksDiscover verified dark web links for secure access to legitimate onion services, ensuring your privacy and safety online.
 Deep Web and Dark WebExplore the deep web and dark web, understanding their differences and significance for privacy-conscious users and researchers.
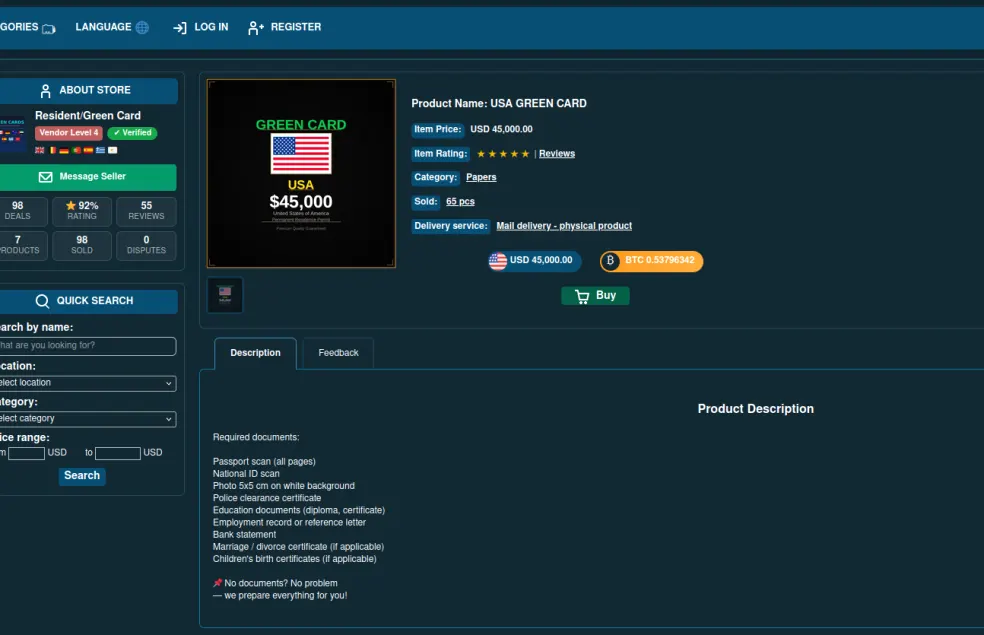 Scammers vs. Reality: The Dark Side of Buying Passports OnlineWe compare darknet passport and green-card listings with real black-market costs, from scam prices of $50 to document costs of $80,000.